Legacy OT security tools create unmanageable operational risk.
Growth in OT, 5G and IoT devices expands the attack surface faster than fragmented tools can defend, while adversaries leverage generative and frontier AI to chain flaws at machine speed.
68%
of organizations do not have complete visibility across all connected OT assets.
55%+
report elevated costs caused by tool sprawl across legacy OT security stacks.
95%
of security leaders worry about weaponized AI targeting critical infrastructure.
The industry's most advanced critical infrastructure defense against frontier AI
When industrial operations depend on uptime, resilience requires asset-centric visibility and active inline prevention in a single platform. Neutralizing AI-driven threats across OT, 5G, IoT and legacy infrastructure demands automated threat prevention powered by operational risk prioritization.
AI-driven critical infrastructure security without operational downtime
Explore the architecture behind each operational advantage to see how native platform engineering turns security goals into continuous, automated protection.
Protect Without Downtime
Shield unpatchable legacy assets inline without invasive agents, reboots or operational downtime. Security without compromise.
+
Protect Without Downtime
HOW WE DO ITInline Network ProtectionEnforce security inline at the network layer to close exposure while critical assets run uninterrupted.
-
Cut Tool Sprawl and Cost
Replace disconnected security point products with one platform that unifies visibility and enforcement to lower operational costs.
+
Cut Tool Sprawl and Cost
HOW WE DO ITUnified Platform EngineCombine asset discovery, risk prioritization and policy enforcement under a single architecture to eliminate alert noise across operations.
-
Neutralize Frontier AI Threats
Counter weaponized AI threats using real-time telemetry and automated protections that continuously evolve as threats mutate.
+
Neutralize Frontier AI Threats
HOW WE DO ITAI-Driven Virtual PatchingBlock zero-day exploits targeting legacy systems inline at machine speed.
-
The State of Critical Infrastructure Cybersecurity Report
A global survey of 1,600 critical infrastructure cybersecurity leaders. Discover your peers’ priorities, including readiness for AI-powered attacks.
Gain continuous, real-time visibility into legacy, proprietary and AI-enabled assets without adding new sensors or disrupting operations.
Prioritize Operational Risk
Weigh vulnerability severity against asset criticality and network exposure to cut alert noise and surface the risks that genuinely threaten availability.
Enforce Inline Protection
Combine asset-centric visibility with active enforcement to stop lateral movement and machine-speed attacks before they reach critical processes.
Protect Unpatchable Assets
Apply AI-driven virtual patching at the network layer to secure OT networks against weaponized frontier AI threats without requiring maintenance downtime.
Resources
Accelerate Your OT Infrastructure Security Strategy
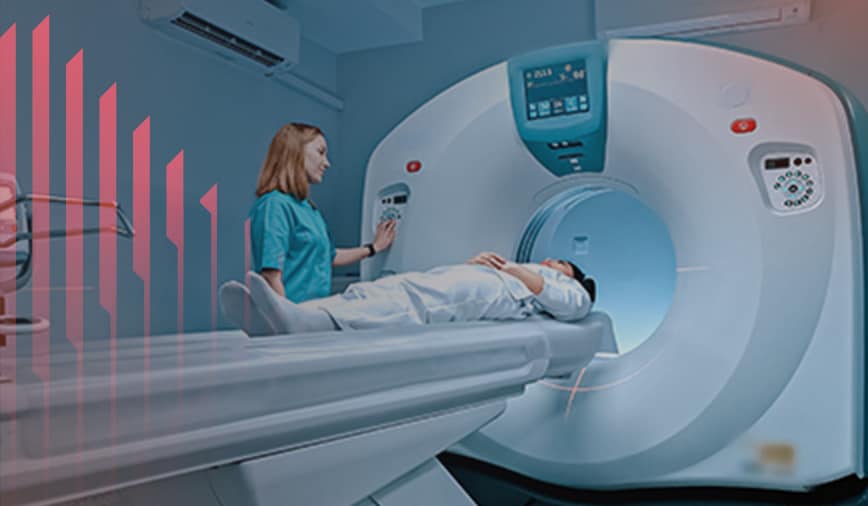
Profile every connected medical device — from infusion pumps to imaging equipment — and reveal active clinical utilization without firmware risk or workflow disruption.
Prioritize Clinical Risk
Assess device criticality, clinical function and attack paths to cut alert noise by 90%, allowing teams to act on risk safely without consulting clinical staff for every decision.
Enforce Native Protection
Apply AI-driven virtual patching for unpatchable CVEs and block 69% more evasive command-and-control traffic inline before it reaches life-sustaining equipment.
Automate Compliance
Seamlessly integrate with clinical CMMS databases (AIMS3, Nuvolo) and generate audit-ready evidence mapped to HIPAA and NIST CSF 2.0 without manual data aggregation.
Resources
Accelerate Your Healthcare Infrastructure Security Strategy
Talk to a critical infrastructure security specialist
Assess your IoMT security posture, uncover visibility and risk gaps and strengthen protection across connected medical devices and clinical environments.
Extend zero trust security across OT enterprise cellular networks with subscriber identity intelligence and inline threat prevention from edge to cloud.
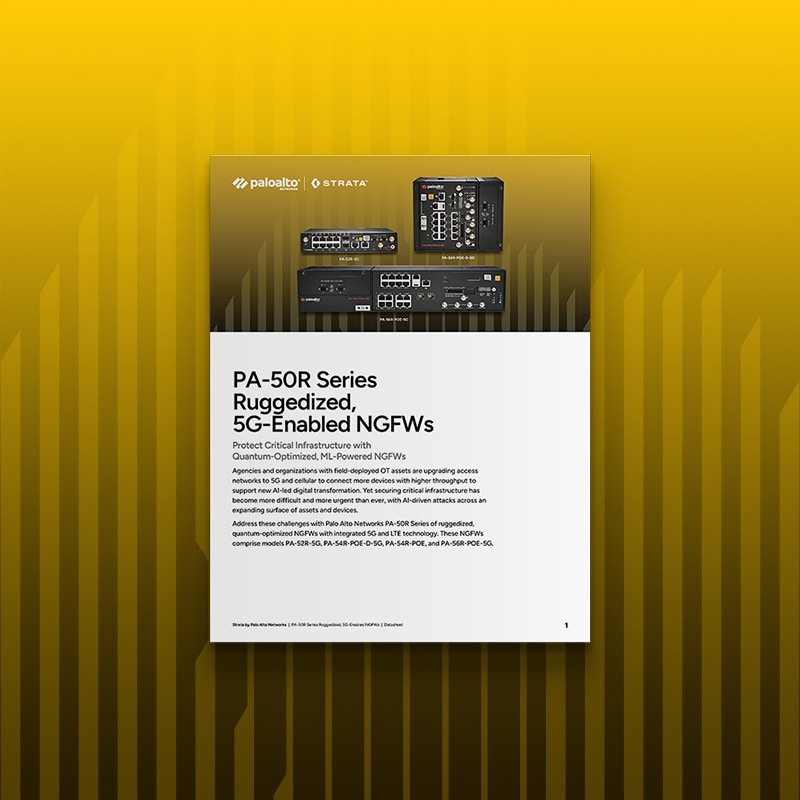
Combine routing, switching, SD-WAN and multiple WAN interfaces in a compact, quantum-optimized, ruggedized NGFW to secure OT and cellular access networks.
Block Machine-Speed Threats
Eliminate human-in-the-loop delay by stopping lateral movement and frontier AI attacks in real time, preventing initial access from turning into operational impact.
Enterprise 5G Security
Edge to cloud access network security eliminates policy fragmentation, inspects traffic inline at the OT layer, enabling zero trust access from 5G edge to core to AI workloads.
Ruggedized NGFWs
New security-first NGFWs are environmentally hardened to protect critical infrastructure at the extreme edge. They are fanless, IP40 rated, and shock- and vibration-certified for the most demanding locations.
Resources
Accelerate Your Enterprise 5G & LTE Security Strategy
Talk to a critical infrastructure security specialist
Assess your private 5G security posture, identify visibility and protection gaps and strengthen security across users, devices and connected infrastructure.
"By leveraging Palo Alto Networks Industrial OT Security, we’re able to get a very accurate and up-to-date real-time inventory of all of our assets on the floor and manage the risk of each device."
Mark Williams, Director, Network Engineering, BorgWarner
Talk to a Critical Infrastructure Security ExpertSchedule a 30-minute strategy call to evaluate your OT, IoT and private 5G posture against machine-speed AI threats and legacy visibility gaps.
THANK YOU
We’ve received your request. A Palo Alto Networks expert will reach out to you shortly.
Resources
Accelerate Your Critical Infrastructure Security Strategy
Access analyst research, buyer’s guides and technical analyses to secure your OT, IoT and private 5G infrastructure in the frontier AI era.
Traditional tools offer passive visibility and detection only, requiring manual intervention to update firewall policies. Palo Alto Networks integrates asset-centric visibility directly with active inline threat prevention in a unified architecture, automatically blocking threats at the network layer.
No. Security functions are delivered natively through the Next-Generation Firewall (NGFW) directly within the existing network path. This eliminates complex integrations while enabling real-time risk prioritization and zero-downtime virtual patching.
Yes. Our ruggedized, hyper-converged, security-first edge firewalls are equipped with integrated 5G/LTE WAN connected to a subscriber identity context (IMEI/IMSI). This provides protection across enterprise 5G environments where SPAN-based tools lack visibility.
Multifactor operational risk prioritization analyzes asset criticality, network exposure and attack paths rather than relying solely on raw CVSS scores. This eliminates up to 90% of noncritical alert noise so teams can focus on actionable threats.
Virtual patching blocks threats at the network perimeter without requiring endpoint agents, asset reboots or maintenance downtime. Threat intelligence updates are automatically delivered across the global network to protect unpatched devices.
Frontier Virtual Patching powered by Frontier AI discovers unknown vulnerabilities and deploys inline protections in hours. By collapsing the industry-average 55-day patching window1 to near-zero, the platform blocks machine-speed attacks and neutralizes weaponized AI exploits before they reach your network.
1. Verizon Data Breach Investigations Report
Get the latest news, invites to events, and threat alerts