The rapid advancement of AI has reshaped the threat landscape in profound ways. Modern attacks are no longer characterized merely by known malware families or static tooling; instead, security teams face a surge in highly bespoke, obfuscated execution chains, targeted supply chain compromises, and rapid post-exploitation techniques designed specifically to blend into normal enterprise noise. Countering this level of complexity demands an evolutionary leap from reactive pattern matching to proactive behavioral understanding.
Advanced attackers rarely rely on known malware techniques alone. Usually they weaponize legitimate administrative tools, hide scripts directly in system memory, and abuse built-in trust to slip past traditional static controls
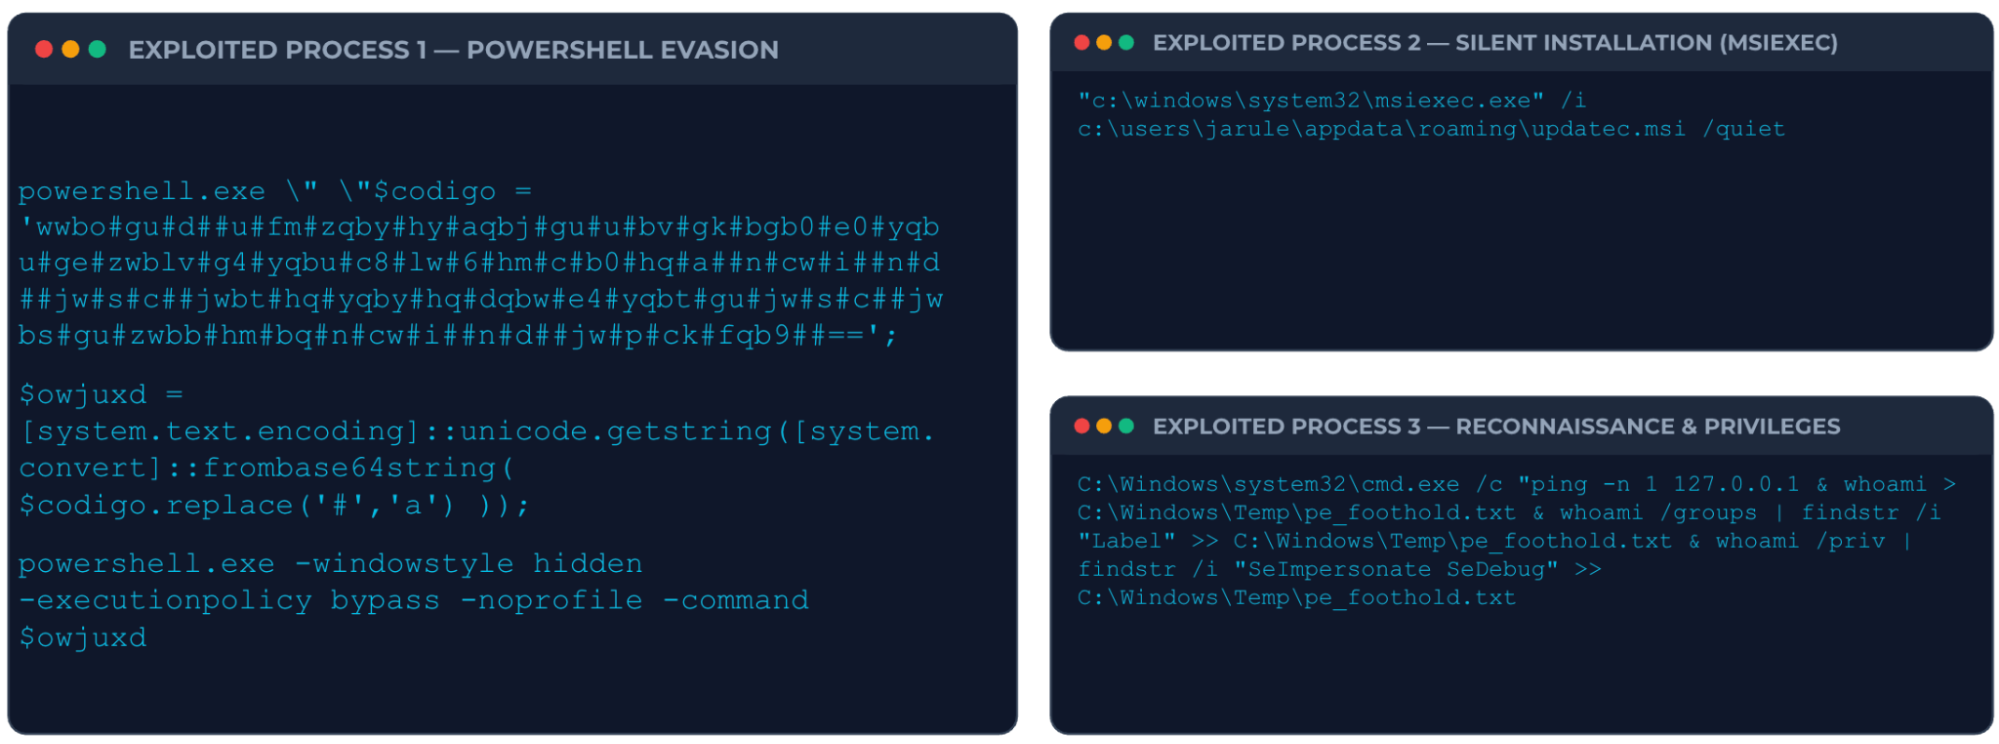
Stopping these evasive tactics has always been the job of Behavioral Threat Protection (BTP) even when attackers constantly disguise their code, underlying behavioural operations like accessing sensitive files or reading process memory remain consistent. Until now, however, that protection came with a significant human bottleneck. Security researchers had to spend thousands of hours digging through telemetry, writing detection logic by hand, and testing policy rollouts. But when adversaries can alter an execution chain in minutes, manual rule writing leaves a dangerous window of exposure between discovery and defense.
Security teams don't just need smarter behavioral protection, they need defense that moves at machine speed.
To stay ahead of threats that dynamically rewrite their own footprints, Cortex XDR is elevating its defense layer with AI-driven Behavioral Threat Protection (BTP) delivering on real-time, data-driven, AI-generated protection to intercept to intercept malicious intent before an attack can establish a foothold.
Rather than relying on manual workflows, AI Driven BTP functions as an automated, 24/7 rule factory. It continuously analyzes threat telemetry across the global Cortex fleet, using machine learning to spot subtle combinations of anomalous activity across terabytes of data. Once the system identifies an emerging technique, it automatically drafts, tests, and validates new prevention rules accelerating rollout times and eliminating unnecessary delays.
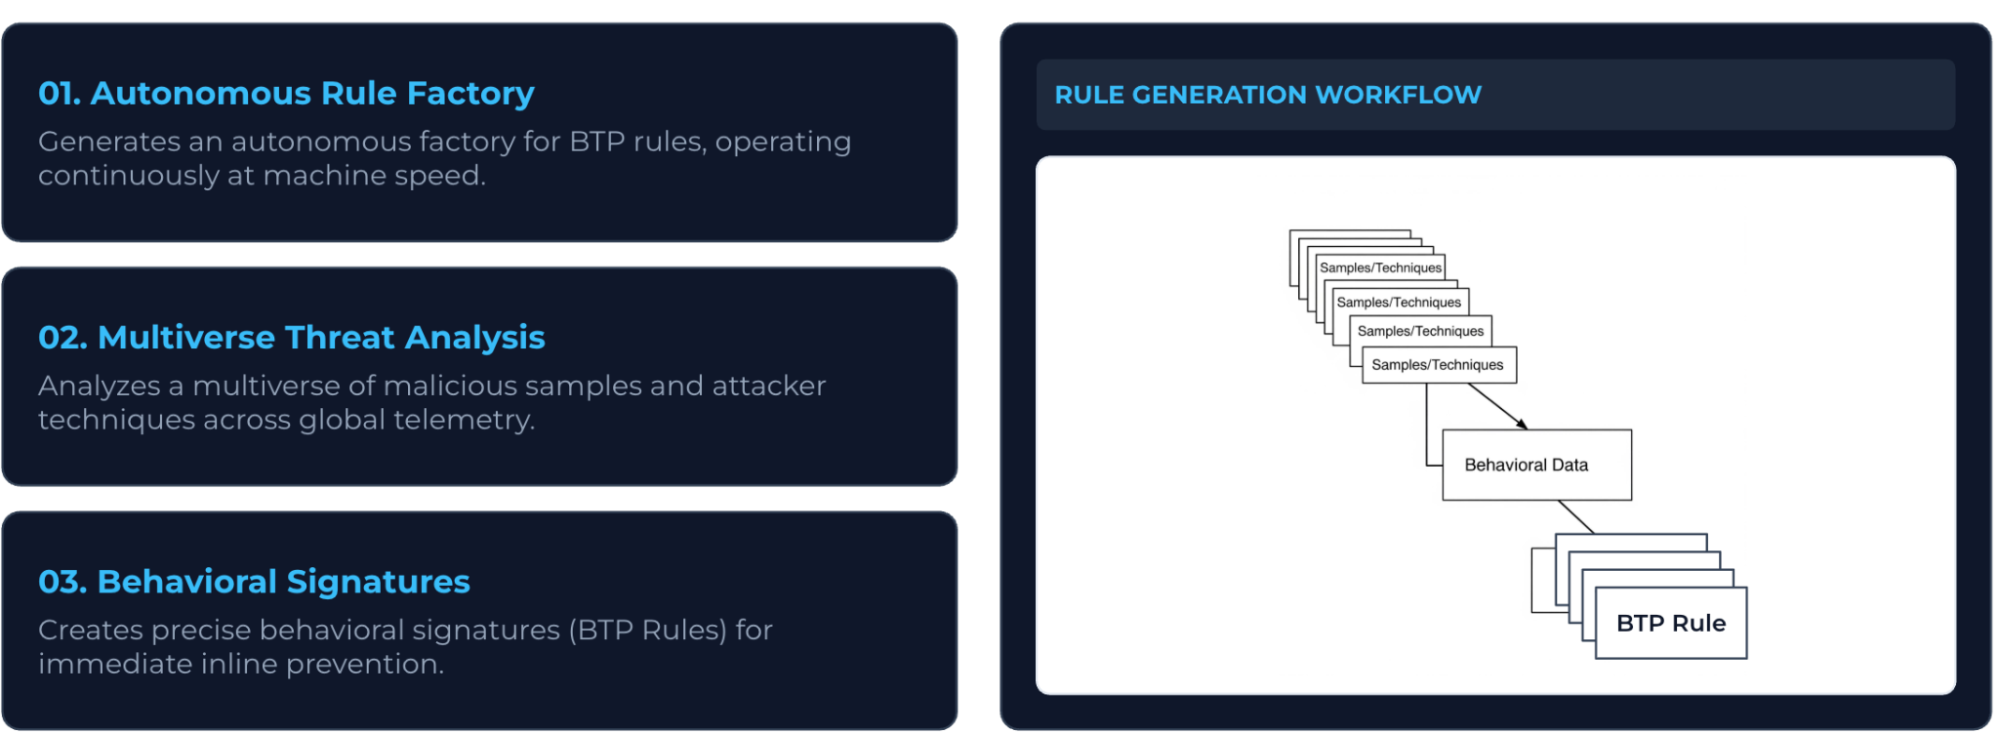
Each update undergoes rigorous validation and a controlled, responsible rollout before being deployed across your fleet. Cortex pushes updates fleet-wide through dynamic content feeds, meaning your teams get ongoing protection updates with zero agent reboots, zero policy reconfiguration, and no manual rule engineering.
This protection works in real time and It stops threats as soon as they execute. For example an attacker leverages normal system tools to hide malicious actions, the AI-driven behavioral threat protection intercepts the malicious sequence, stopping the attack in real time.
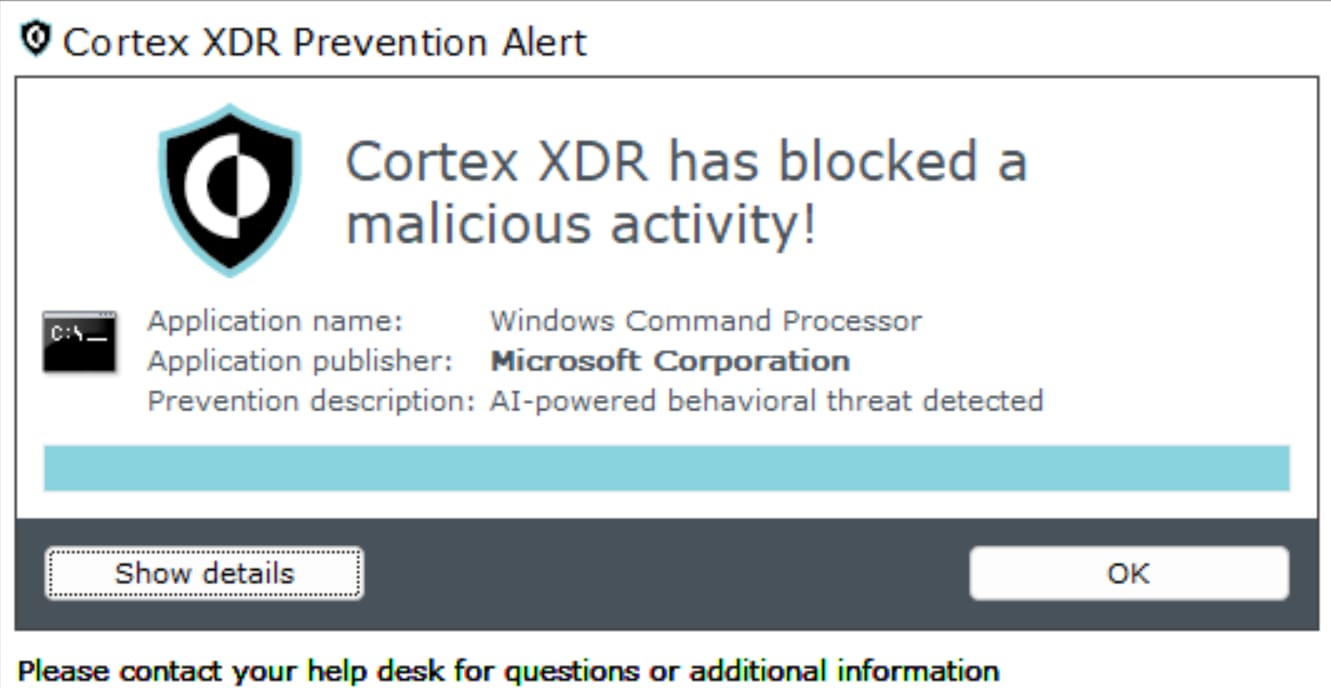
Enforcement happens automatically, but your analysts never lose context. The Cortex XDR incident card lays out the full execution tree, details the affected hosts, and explains the exact behavioral logic that triggered the block.
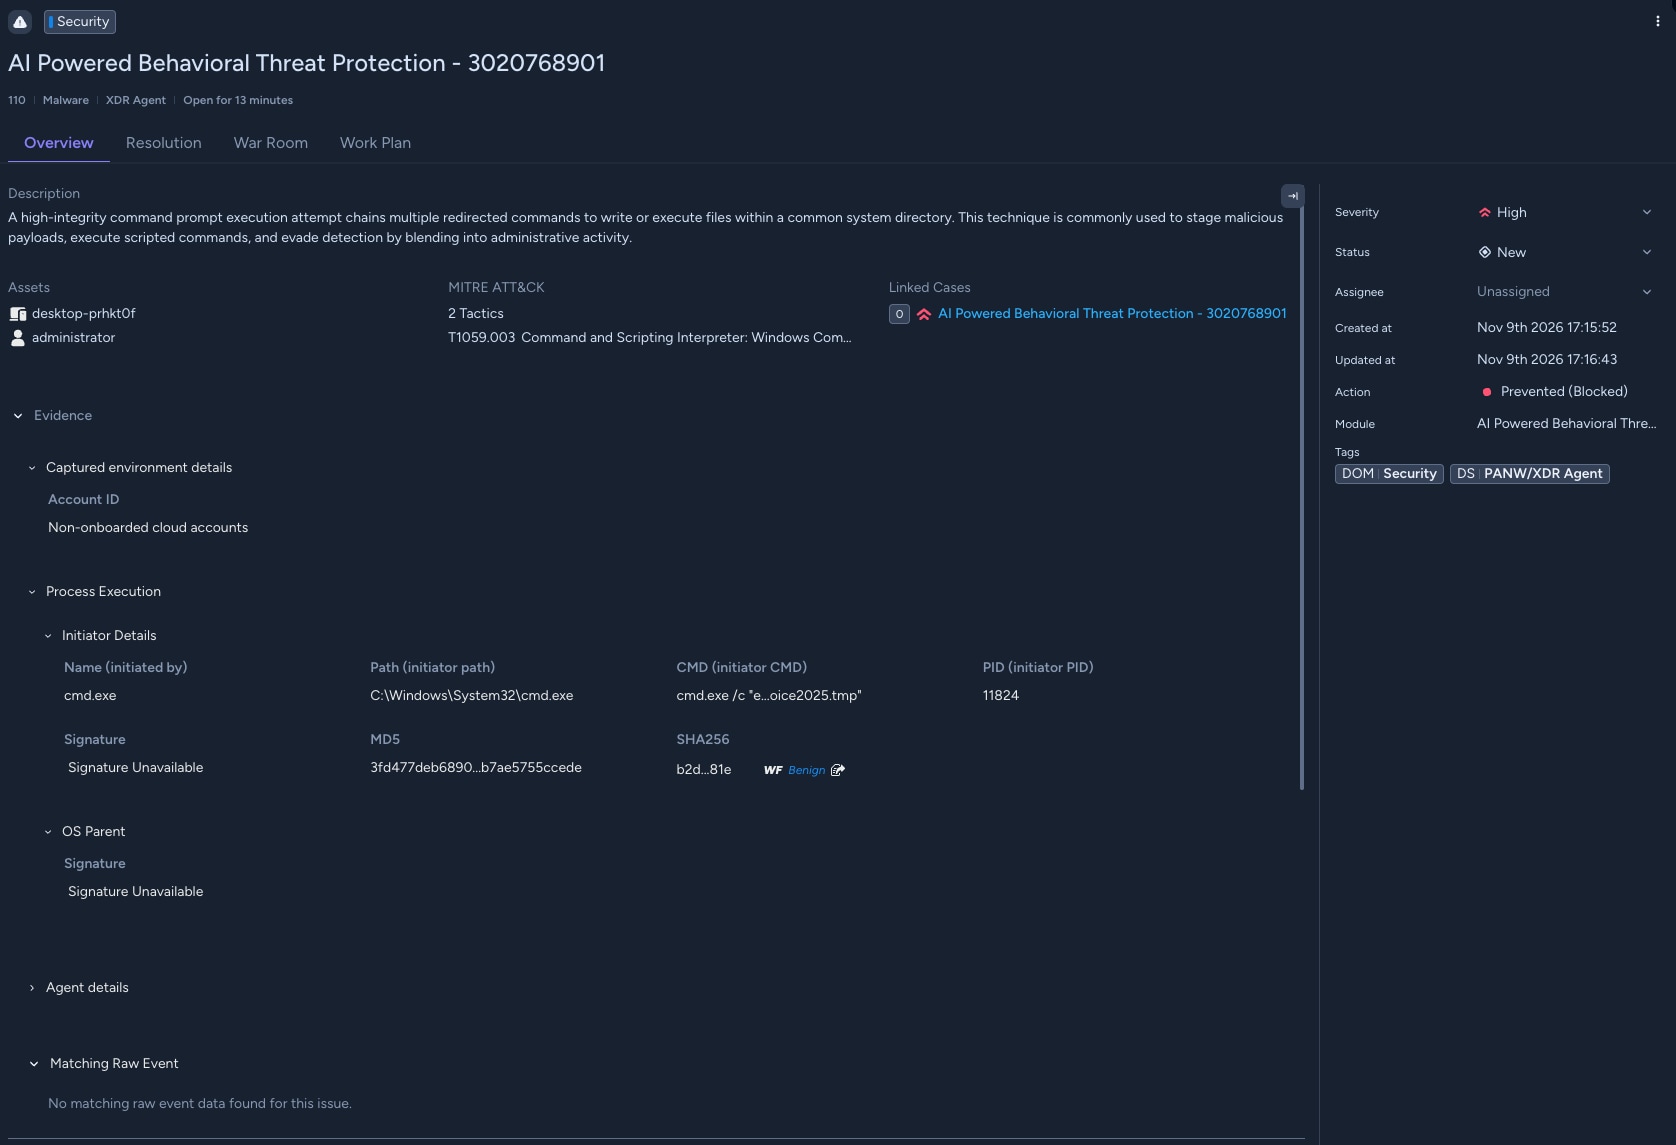
By automating rule creation from start to finish, Cortex XDR turns endpoint defense into a self-updating, zero-touch shield that adapts as fast as modern threats do.
Want to see how AI Driven BTP works inside your existing Malware Prevention Profiles? Reach out to your account team or request a personalized demo today.