Search
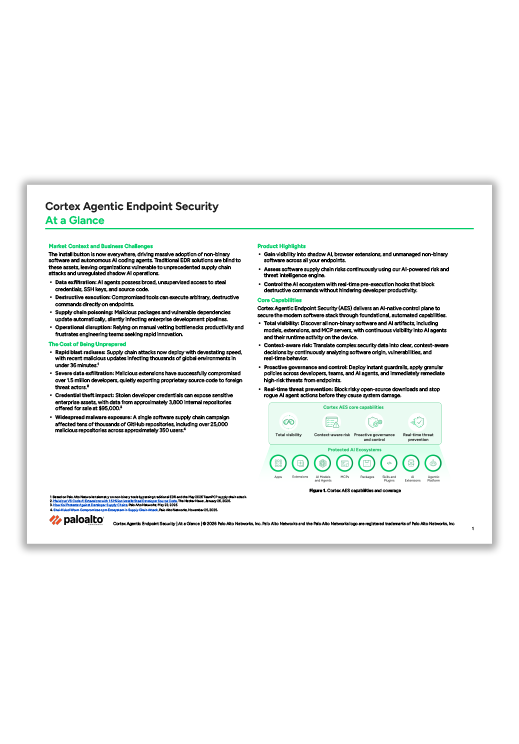
Secure the agentic endpoint with total visibility and real-time control.
 |  | |
|---|---|---|
AI-Native Total Visibility | Risk intelligence on the full supply chain Complete agentic context with real-time enforcement to secure all elements of the agentic endpoint. | No preexecution native risk scoring CrowdStrike relies on post-breach detections and not every AI artifact has version-specific risk context. |
Proactive Governance and Control | Policy-driven AI guardrails Control the AI ecosystem through policy-driven guardrails, blocking risky components at the point of entry and continuously monitoring them as conditions change. | Governance that acts too late Reactive detection and response that enforces after a threat has been flagged. |
Real-Time Prevention | Preexecution enforcement Block risky agent behavior before execution or software before installation, with zero latency. | Limited runtime controls and marketplace risk Lack of inline enforcement and inconsistent across agentic endpoints and artifacts. |
Secure Every Agent | Verified agents, controlled access Know which agent is acting and decide what it can reach, from data and tools to MCP servers, with Prisma® AIRS™. | Spotty enforcement dependent on setup Coverage changes with each integration and some only watch instead of block. |
Govern AI Usage | The control plane for the AI enterprise See who uses which AI and what it costs, and enforce policy across every interaction with Prisma AIRS. | No AI gateway A centralized gateway for AI and MCP traffic is not available. |
Seamless Configuration | Easy deployment and zero developer friction Balance security and productivity from day one, with zero workflow disruption blind spots. | Requires manual wrappers with local proxies Security shouldn’t be an arts and crafts project stitching together manual configuration, activity logs and MCP wrappers. |
Protection and Platform Support | Breadth and depth of visibility and enforcement Wherever your employees may work, Cortex AES protects across all environments. | Lack of maturity across OS environments and browser protection Fails to support macOS and Linux for network-level AI inspection, with limited browser enforcement only for managed Chrome and Edge. |
Install attempts blocked directly by the platform
“Agentic AI presents tremendous opportunity for the enterprise, yet they create a new attack surface that traditional security tools were not built to detect. These agents operate with access to critical systems and sensitive data, creating the ultimate insider threat. With [Cortex AES] we are delivering the only solution I've seen to secure vibe coding and agentic AI at the endpoint, so our customers don't have to choose between innovation and security.”
“The first time we ran Koi, we uncovered an entire landscape of marketplaces and risks we didn't even know existed. We’ve moved from total blind spots to complete visibility and enforcement.”
“Marketplace governance is what sold me. Being able to write policy across browser and IDE extensions instead of just blocking known-bad ones, and having that in the same place as package and model visibility — that's the win for us.”
“Koi Agentic Endpoint Security is one of my favorite tools because it gives me visibility and governance into areas I didn't have before — the marketplaces, extensions, and packages my people pull from every day.”
“Previously, we had zero visibility, zero classification for AI, marketplaces, and packages. We couldn’t do any cooldown protection. Now Koi Agentic Endpoint Security does all that for me—quickly and easily.”
“Agentic AI presents tremendous opportunity for the enterprise, yet they create a new attack surface that traditional security tools were not built to detect. These agents operate with access to critical systems and sensitive data, creating the ultimate insider threat. With [Cortex AES] we are delivering the only solution I've seen to secure vibe coding and agentic AI at the endpoint, so our customers don't have to choose between innovation and security.”
“The first time we ran Koi, we uncovered an entire landscape of marketplaces and risks we didn't even know existed. We’ve moved from total blind spots to complete visibility and enforcement.”
“Marketplace governance is what sold me. Being able to write policy across browser and IDE extensions instead of just blocking known-bad ones, and having that in the same place as package and model visibility — that's the win for us.”
“Koi Agentic Endpoint Security is one of my favorite tools because it gives me visibility and governance into areas I didn't have before — the marketplaces, extensions, and packages my people pull from every day.”
“Previously, we had zero visibility, zero classification for AI, marketplaces, and packages. We couldn’t do any cooldown protection. Now Koi Agentic Endpoint Security does all that for me—quickly and easily.”