With native Cortex Agentic Endpoint Security capabilities and Prisma AIRS integration, Cortex XSIAM brings comprehensive enterprise AI protection to the SOC.
AI is changing how business gets done. Today, autonomous agents write code, access sensitive information, connect to enterprise applications, and execute increasingly complex workflows. They unlock new levels of productivity and innovation, but also introduce security risks that traditional SOCs were never designed to address.
The modern SOC has a brand new responsibility: defending the rapidly expanding world of AI agents, applications, and models. As AI becomes central to business operations, the SOC must expand its protection to AI while continuing to defend the broader enterprise.
Enterprise AI Is Redefining the Attack Surface
AI is transforming the enterprise endpoint, introducing agents, models, and tools that execute commands, access sensitive data, and act with real user privileges. These capabilities create new attack paths as adversaries use AI to accelerate attacks, with data exfiltration now up to 4x faster according to Unit 42 threat research.
Malicious extensions, compromised MCP servers, and software dependencies can introduce threats, while prompt injection can manipulate agents into unauthorized actions. A compromised agent can access credentials, move across cloud environments, and expose sensitive data.
These threats extend well beyond individual AI applications, spanning endpoints, networks, cloud environments, and identities. Legacy SIEMs often lack the context to connect AI activity with threats across the broader enterprise.
Securing enterprise AI requires protection across every layer, from AI agents and applications to the underlying infrastructure, with unified visibility, detection, and response across the SOC.
Extending the Agentic SOC to the AI Endpoint
Cortex XSIAM brings AI-driven detection, investigation, and response together in a unified platform to power the agentic SOC. Now, with Cortex Agentic Endpoint Security integrated into the Cortex XDR sensor, Cortex XSIAM customers using XDR can protect AI running on endpoints through proactive risk assessment, prevention, and runtime security.
This native integration enables teams to:
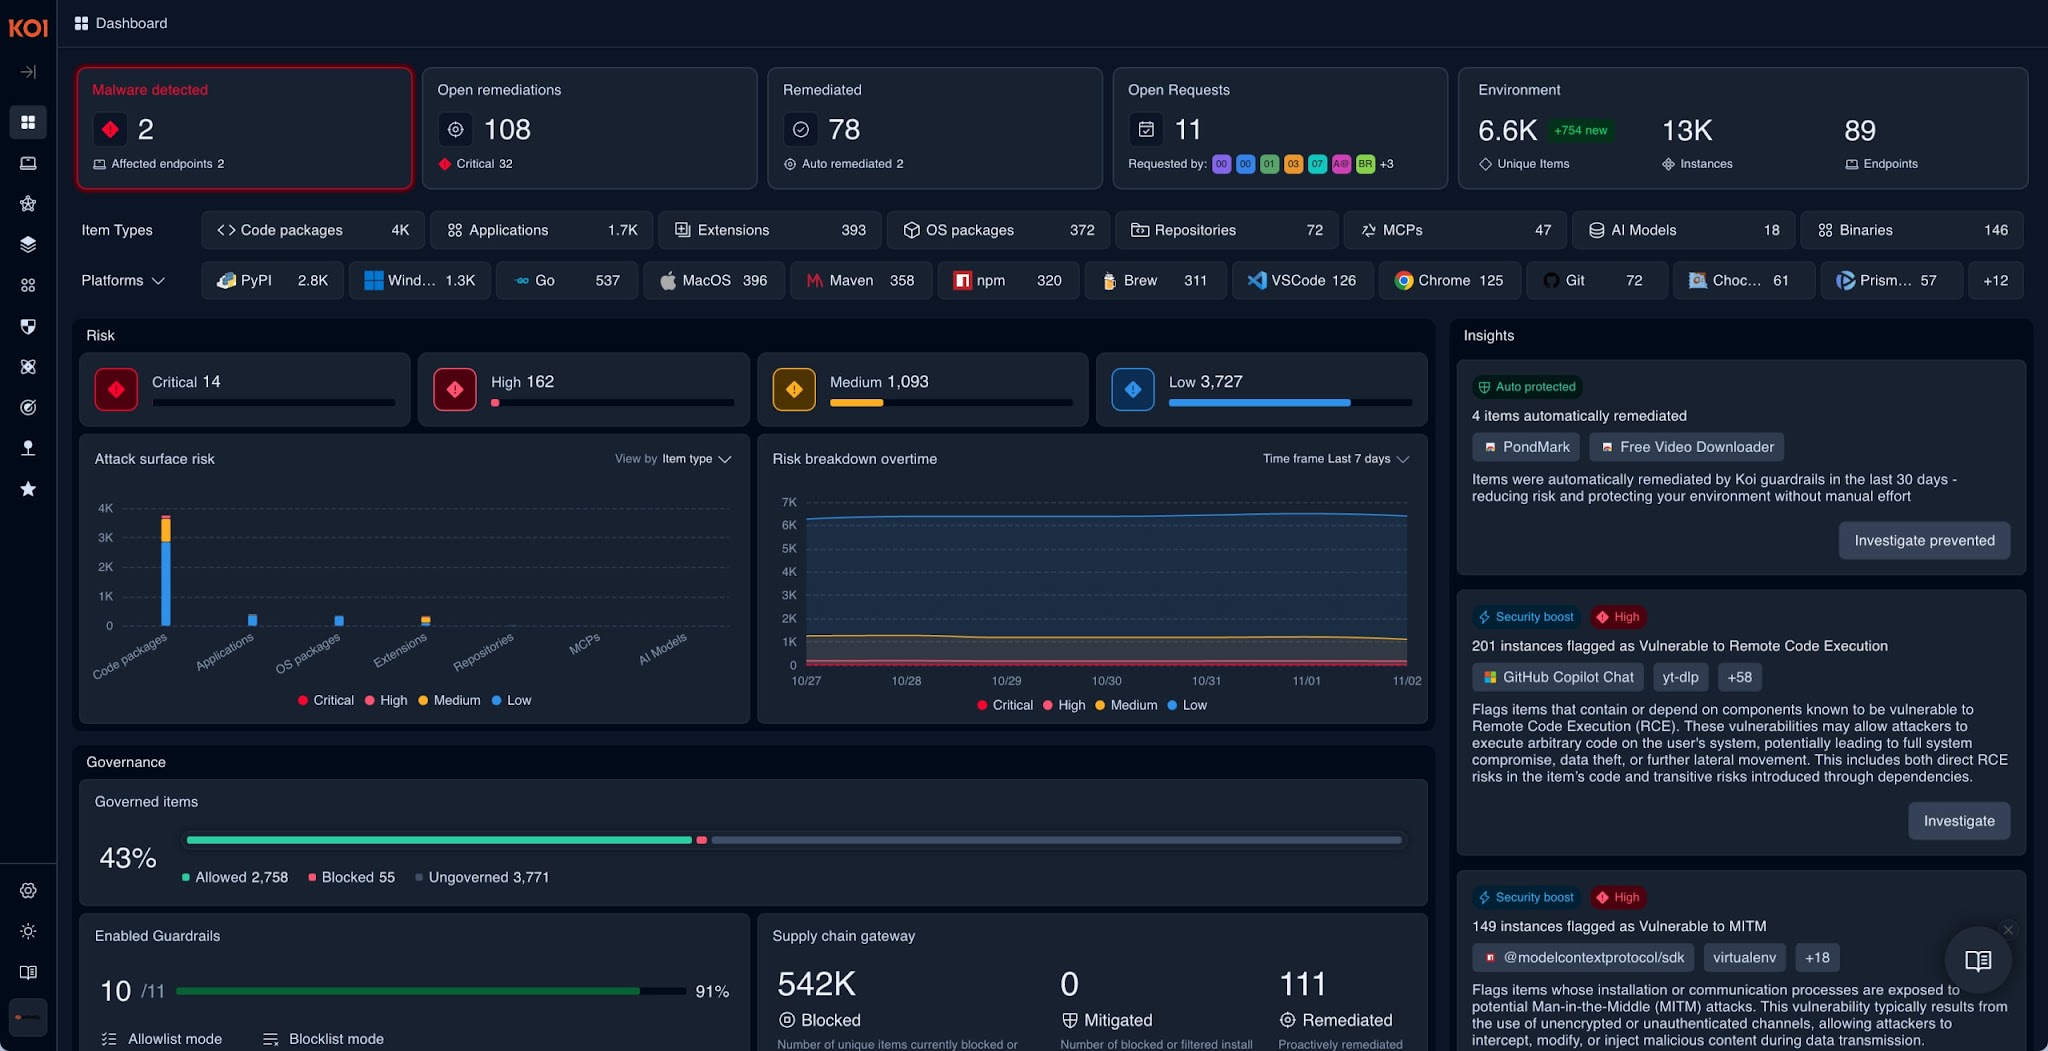
- Discover AI assets and exposure at the endpoint. Gain visibility into AI agents, models, IDE extensions, MCP servers, and software dependencies to uncover potential threats and security gaps.
- Detect and stop rogue AI agents. Identify malicious code and unauthorized agent behavior, enforce real-time guardrails, and automate protective actions before threats escalate.
- Connect AI activity across the enterprise. Cortex XSIAM correlates AI-specific threats and agent actions with broader enterprise activity to uncover attacks, trace their impact, accelerate investigations, and orchestrate response.
Trusted AI tools can quickly become Trojan horses. In October 2026, malicious Claude Code extensions distributed through Cursor's marketplace potentially exposed 5,000 developers in just 11 hours. Cortex Agentic Endpoint Security helps stop these threats at the source, identifying compromised components and blocking malicious code before it executes.
We’re also extending Cortex XSIAM’s protection to desktop AI agents through a new Cortex XDR integration with Claude Cowork, providing runtime visibility into agent activity and detecting threats within the virtual machines where they operate.
Unifying AI Security with Cortex XSIAM and Prisma AIRS
Protecting AI at the endpoint is only part of the equation. Security teams must also correlate AI-specific threats, such as prompt injection, with broader enterprise activity to understand what AI agents actually did, trace their actions, and assess the full impact.
With Cortex XSIAM 4.0’s new Prisma AIRS integration, organizations can bring AI Runtime Security detections, AI Supply Chain Security model scan results, and AI Red Teaming findings into the SOC. Cortex XSIAM correlates threats such as prompt injection, jailbreak attempts, tool misuse, and data leakage with endpoint, network, cloud, and identity activity across its 1,100+ integrations. Security teams can trace AI-specific threats to actions taken across the enterprise, understand their impact, and respond with full context.
Consider a compromised AI agent that accesses sensitive credentials and attempts to retrieve data from a cloud repository. Cortex XSIAM can help connect the AI security signals with endpoint, identity, and cloud activity, giving analysts the visibility they need to investigate the incident and coordinate response.
This integration lets security teams:
- Unify AI threats with enterprise context. Correlate Prisma AIRS telemetry on prompt injection, data leakage, and more with endpoint, network, cloud, and identity data for a unified view of threats across AI and traditional environments.
- Detect and investigate AI threats. Connect suspicious AI interactions with activity across the enterprise, using AI-driven analytics to uncover attack patterns, trace their origins, and assess their impact.
- Automate response. Orchestrate remediation across the security ecosystem with AI-powered workflow automation and agentic response.

Rather than managing enterprise AI security separately, organizations can bring this information into Cortex XSIAM, the same agentic SOC that protects the rest of their business.
The Agentic SOC Must Protect Enterprise AI
As AI transforms the enterprise, the SOC must evolve to safeguard it. The next generation of SIEM must go beyond collecting logs and correlating alerts to protect the AI agents, applications, and infrastructure redefining how businesses operate.
Palo Alto Networks brings together Cortex Agentic Endpoint Security in Cortex XDR, Prisma AIRS real-time inspection of AI interactions, and Cortex XSIAM's AI-driven analytics and automation to protect enterprise AI, from proactive threat prevention to detection, investigation, and response across the enterprise.

The agentic SOC must do more than use AI to defend the enterprise. It must defend enterprise AI itself.
See the next generation of security operations in action. Go behind the scenes of the agentic SOC with the latest Cortex XSIAM innovations, expert insights, and a live demo. Watch Agentic SOC Undercover, part of our Cortex Forward virtual event series, on demand.